API Security Compliance for PCI DSS, GDPR, and SOC 2: Complete Guide
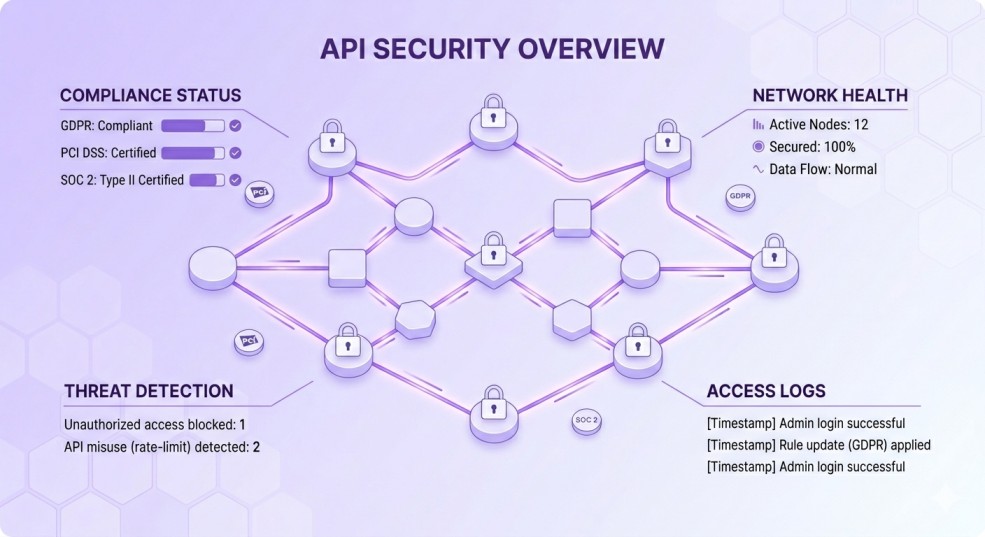
APIs power nearly every modern application. They handle authentication, payment processing, personal data exchange, and core business logic. But as API adoption grows, so does the attack surface they expose.
For organizations operating under PCI DSS, GDPR, or SOC 2, API security is not optional. These frameworks explicitly require data protection in transit, enforced access controls, continuous monitoring, and validated security controls. Organizations that treat API security as a development concern rather than a compliance obligation consistently face audit findings, delayed certifications, and in the worst cases, data breaches that trigger regulatory penalties.
This guide breaks down exactly what each framework requires from your APIs, what risks create the most compliance exposure, and how to build a testing program that keeps you audit-ready year-round.
Why API Security Compliance Matters More Than Ever?
Modern applications expose far more API surface area than most security teams fully account for. A single customer-facing product may rely on dozens of internal and third-party API endpoints, each representing a potential entry point for attackers.
API security testing has moved from a nice-to-have to a baseline compliance requirement because frameworks like PCI DSS, GDPR, and SOC 2 have caught up to how modern software actually works. They no longer accept perimeter-focused security programs that ignore API layers.
The consequences of non-compliance are concrete:
PCI DSS violations can result in fines, mandatory forensic audits, and loss of card processing privileges
GDPR breaches carry penalties of up to 4% of global annual revenue
SOC 2 findings delay certification and erode customer trust
Compliance frameworks share a consistent set of API security expectations, even if they express them differently.
Core API Security Requirements Across All Three Frameworks
Although PCI DSS, GDPR, and SOC 2 have different objectives, they converge on the same set of technical API security controls. Organizations that satisfy these shared requirements build a foundation that supports all three frameworks simultaneously.
Control Area | PCI DSS | GDPR | SOC 2 |
Authentication and Authorization | Required | Required | Required |
Encryption in Transit (TLS) | Mandatory | Required | Required |
Input Validation | Explicitly required | Best practice | Expected |
Rate Limiting and Abuse Prevention | Required | Recommended | Expected |
Logging and Audit Trails | Mandatory | Mandatory | Required |
Vulnerability Management | Required | Required | Required |
Shared Security Controls
Strong authentication and authorization on every endpoint
Encryption of sensitive data in transit and at rest
Input validation to prevent injection and manipulation attacks
Rate limiting to prevent abuse and denial-of-service conditions
Detailed logging of API activity for audit trails and breach detection
Regular security testing and structured remediation tracking
Understanding API authentication and authorization vulnerabilities is foundational to satisfying all three frameworks. Broken object-level authorization (BOLA), excessive permissions, and missing function-level controls are among the most cited findings in compliance audits.
API Security Requirements for PCI DSS Compliance
PCI DSS is built around protecting cardholder data wherever it is stored, processed, or transmitted. APIs involved in payment flows sit at the center of this requirement. They connect applications to payment gateways, handle transaction data, and authenticate users against payment services.
What PCI DSS Requires from APIs?
Authentication and access control: Every API endpoint that handles payment data must enforce strong authentication. OAuth tokens, API keys with proper rotation policies, and mutual TLS are common controls. Anonymous or weakly authenticated endpoints in a cardholder data environment are a direct PCI violation.
Encryption: All payment-related data transmitted through APIs must be encrypted using TLS 1.2 or higher. Unencrypted endpoints in scope of cardholder data are an automatic audit failure.
Input validation: APIs must validate and sanitize all incoming data to prevent injection attacks that could expose or manipulate payment records.
Least privilege: API access should be scoped to the minimum permissions required. Overly permissive tokens or service accounts that access cardholder data beyond their functional need create unnecessary risk.
Logging and monitoring: All API transactions in the payment environment must be logged, tamper-resistant, and retained for audit purposes.
PCI DSS API Security Controls Summary
Enforce strong authentication using OAuth, signed tokens, or API keys with rotation
Encrypt all payment API traffic with TLS 1.2 or higher
Validate and sanitize all input to prevent injection vulnerabilities
Apply least-privilege access scoping across all API credentials
Maintain detailed, tamper-resistant logs of all API transactions
Exposed payment APIs are among the highest-value targets for attackers. A single weak authentication implementation or unencrypted endpoint can lead to large-scale cardholder data exposure, triggering both immediate financial penalties and long-term reputational damage.
API Security Requirements for GDPR Compliance
GDPR governs how personal data is collected, processed, stored, and accessed. APIs that handle personal data names, email addresses, location data, health records, and behavioral data must be architected and secured with privacy as a core design principle.
What GDPR Requires from APIs?
Data minimization: APIs should only return the data fields necessary for their stated function. Endpoints that expose full user records when only a user ID is needed violate the data minimization principle and increase breach impact.
Access restriction: Personal data endpoints must enforce strict authentication and authorization. Users and services should only access data they are explicitly permitted to view.
Encryption: Personal data transmitted through APIs must be encrypted in transit. Storage-layer encryption is also expected for sensitive personal data.
Audit logging: GDPR requires organizations to demonstrate who accessed personal data, when, and for what purpose. API-level logging that captures access events, data subjects, and actions is critical for meeting this requirement.
Breach detection and response: APIs must include monitoring capable of detecting unauthorized access or anomalous data access patterns so that breach notifications can be issued within GDPR's 72-hour window.
GDPR API Security Controls Summary
Implement data minimization at the API response level
Enforce role-based access control for all personal data endpoints
Encrypt personal data in transit and at rest
Log all access to personal data with sufficient detail for audit and breach reporting
Monitor API traffic for anomalous patterns indicative of unauthorized access
Privacy by design is not just a philosophical principle under GDPR, it is an enforceable requirement. APIs that were not designed with data minimization and access restriction built in from the start typically require significant remediation to reach compliance.
API Security Requirements for SOC 2 Compliance
SOC 2 evaluates operational security against five Trust Services Criteria: security, availability, processing integrity, confidentiality, and privacy. APIs directly affect all five. Weak API security can compromise data confidentiality, disrupt availability, and undermine processing integrity, making APIs a focal point for SOC 2 auditors.
What SOC 2 Requires from APIs?
Access management (CC6): APIs must enforce authentication and authorization consistent with the organization's access management policies. Auditors look for evidence that unauthorized access is actively prevented, not just theoretically restricted.
Continuous monitoring (CC7): SOC 2 requires ongoing monitoring of system operations, which includes API traffic. Logging, anomaly detection, and alerting on suspicious API activity demonstrate compliance with this criterion.
Vulnerability management (CC7.1): Organizations must continuously identify and remediate vulnerabilities. This includes APIs. Periodic vulnerability scanning and penetration testing of API surfaces are expected.
Change management (CC8): New API deployments and updates must be evaluated for security before release. Automated testing in deployment pipelines satisfies this requirement.
SOC 2 API Security Controls Summary
Enforce authentication and authorization aligned with access management policies
Continuously monitor API traffic for anomalies and suspicious activity
Conduct regular API vulnerability scanning and penetration testing
Integrate security validation into API deployment workflows
Maintain detailed logs that support audit and incident investigation
The OWASP API Top 10 provides a practical reference for the vulnerability classes that SOC 2 auditors expect organizations to assess and address. Findings in categories like broken authentication, excessive data exposure, and security misconfiguration are direct compliance risks.
Common API Security Risks That Create Compliance Exposure
Understanding where APIs most commonly fail is essential for building a testing program that actually reduces compliance risk. Most API security incidents trace back to a small set of recurring vulnerability patterns.
Broken Authentication and Authorization
The most frequently exploited API vulnerability class. This includes missing authentication on endpoints, tokens with excessive permissions, and broken object-level authorization that allows users to access other users' data. These vulnerabilities directly violate PCI DSS access control requirements, GDPR access restriction obligations, and SOC 2 Trust Services Criteria around logical access.
Excessive Data Exposure
APIs that return more data than is functionally necessary create unnecessary compliance risk. A response that includes internal user IDs, system metadata, or sensitive fields not required by the consuming application violates GDPR's data minimization principle and increases the impact of any breach.
Injection Vulnerabilities
SQL injection, command injection, and other input validation failures in API endpoints can expose cardholder data, personal data, and internal systems. PCI DSS explicitly requires input validation; injection vulnerabilities are a direct non-compliance finding.
Shadow APIs and Unmanaged Endpoints
APIs that exist outside of formal inventory and governance processes, legacy endpoints, undocumented development interfaces, third-party integrations that were never formally reviewed, represent blind spots in the compliance program. If it is not in scope, it cannot be tested or monitored.
Lack of Rate Limiting
APIs without rate limiting are vulnerable to abuse, credential stuffing, and enumeration attacks. Beyond the security risk, the absence of rate limiting controls is frequently cited in PCI DSS and SOC 2 audits as a control gap.
Insufficient Logging and Monitoring
Auditors across all three frameworks expect organizations to demonstrate that API activity is logged and that anomalous behavior triggers investigation. APIs with incomplete or absent logging cannot satisfy breach detection requirements under GDPR or monitoring requirements under SOC 2.
API Security Testing: The Core of a Compliance Program
Policy documentation and architectural controls alone do not satisfy PCI DSS, GDPR, or SOC 2 auditors. All three frameworks expect technical validation that controls work as intended. API security testing provides this validation through structured, repeatable assessments that generate audit-ready evidence.
Automated API Scanning vs. Manual API Penetration Testing
A common source of confusion in compliance programs is whether automated scanning is sufficient or whether manual penetration testing is required. The honest answer is that both serve different purposes and neither replaces the other. A detailed comparison is available in our guide on API scan vs API pentest.
Automated API scanning uses tools to identify known vulnerability patterns across API endpoints. It provides broad coverage, can be run continuously, and integrates into CI/CD pipelines. API scan services are particularly valuable for ongoing compliance monitoring because they detect new vulnerabilities introduced by code changes before they reach production.
Manual API penetration testing goes further by simulating how a real attacker would chain vulnerabilities, abuse business logic, and bypass security controls. It uncovers complex issues that automated tools miss: insecure direct object references, privilege escalation paths, and multi-step authentication bypasses. The API pentest methodology used by experienced testers covers the full OWASP API Top 10 and goes beyond it to test environment-specific logic and integrations.
For compliance purposes, most frameworks expect both. Automated scanning satisfies continuous monitoring requirements. Manual penetration testing satisfies the deeper validation requirements that auditors use to evaluate whether controls actually hold under realistic attack conditions.
API Fuzzing
API fuzzing is a specialized testing technique that sends unexpected, malformed, or random inputs to API endpoints to identify crashes, unexpected behaviors, and input validation failures. It is particularly effective at uncovering vulnerabilities that standard scanning misses: edge-case injection flaws, parser errors, and logic failures triggered by unusual input combinations.
For organizations handling payment data under PCI DSS, fuzzing provides strong evidence that input validation controls are robust across a broad input space, not just against known attack signatures.
Authentication and Authorization Testing
Given that broken authentication and authorization are the most common API compliance findings, dedicated testing of these controls is essential. This involves verifying that:
Unauthenticated requests to protected endpoints are rejected
Tokens cannot be used beyond their intended scope
Object-level authorization prevents cross-user data access
Privilege escalation through parameter manipulation is not possible
Key Testing Approaches for Compliance
Testing Type | What It Covers | Compliance Value |
Automated API Scanning | Known vulnerability patterns, misconfigurations | Continuous monitoring evidence |
Manual API Penetration Testing | Business logic, complex attack chains | Control effectiveness validation |
API Fuzzing | Input validation, parser robustness | PCI DSS input control evidence |
Auth and Authz Testing | Access control effectiveness | Cross-framework compliance evidence |
Schema Validation Testing | Endpoint conformance, data leakage | GDPR data minimization evidence |
Integrating API Security into CI/CD Pipelines
Compliance is a continuous state, not a point-in-time achievement. Organizations that deploy APIs frequently, which is nearly all organizations using modern development practices, cannot rely on quarterly assessments to maintain compliance. New code can introduce new vulnerabilities with every deployment.
API security in CI/CD pipelines addresses this challenge by embedding automated security validation directly into the deployment workflow. Every time an API change is committed or deployed, security checks run automatically, catching vulnerabilities before they reach production.
What CI/CD API Security Integration Enables
Early detection: Vulnerabilities are caught in development, where they are cheapest to fix
Faster remediation cycles: Developers address issues in context, with immediate feedback
Continuous compliance readiness: Every deployment is tested, eliminating gaps between periodic assessments
Reduced audit preparation burden: Continuous testing generates an ongoing evidence trail rather than a one-time report
The recommended architecture combines automated API scanning in CI/CD pipelines with periodic manual penetration testing (typically quarterly or semi-annually). Automated testing provides the frequency and breadth that continuous compliance requires. Manual testing provides the depth and sophistication that automated tools cannot replicate.
Organizations that adopt DevSecOps practices achieve more scalable compliance programs because security becomes part of the delivery process rather than a separate gate. Audit readiness becomes a continuous state rather than a sprint before each certification cycle.
What Auditors Expect from Your API Security Program?
Auditors evaluating API security compliance look for evidence across four dimensions:
1. Scope completeness: Have all API surfaces been identified and included in the security program? This includes internal APIs, partner APIs, legacy endpoints, and third-party integrations. Shadow APIs and undocumented endpoints are an immediate concern.
2. Testing rigor: Is the testing methodology appropriate for the risk? A compliance program that relies only on automated scanning without manual penetration testing will face scrutiny. Auditors look for evidence that testing covers the full OWASP API Top 10 and uses methods appropriate for the environment.
3. Remediation evidence: Identifying vulnerabilities is only half the requirement. Auditors need to see that findings are tracked, remediated, and verified through retesting. A vulnerability report without a remediation record is incomplete evidence.
4. Continuous validation: One test per year is insufficient. Auditors expect evidence of ongoing monitoring and testing, particularly for organizations with frequent deployment cycles.
Elements of an Audit-Ready API Security Report
Defined scope covering all API surfaces tested
Testing methodology aligned with OWASP API Top 10 and relevant frameworks
Detailed findings with severity ratings, evidence, and business impact
Mapping of findings to specific compliance controls (PCI requirement, GDPR article, SOC 2 TSC)
Remediation recommendations prioritized by risk
Retesting results confirming vulnerability resolution
Choosing the Right API Security Partner
Not all security providers are equipped to support compliance-driven API security. Many deliver generic vulnerability scans with reports that satisfy no auditor and provide no actionable guidance for development teams.
What to Look for in a Compliance-Focused API Security Provider?
Demonstrated experience with PCI DSS, GDPR, and SOC 2 requirements
Ability to perform both automated scanning and manual penetration testing
API-specific methodologies covering the OWASP API Top 10 and beyond
Compliance-aligned reporting that maps findings to specific framework controls
Support for CI/CD integration and DevSecOps workflows
Retesting capabilities to validate remediation
The right partner reduces the time and effort required to achieve certification by delivering evidence that auditors can use directly, rather than requiring internal teams to interpret and translate technical findings into compliance language.
How NyxSentinel Supports API Security Compliance?
NyxSentinel delivers API security programs designed for the compliance requirements of PCI DSS, GDPR, and SOC 2 in modern, API-heavy architectures.
Core Capabilities
Continuous API vulnerability scanning provides ongoing visibility into API security posture, detecting new vulnerabilities introduced by code changes before they reach production and create compliance exposure.
Deep manual API penetration testing simulates real-world attack scenarios against your API surfaces, uncovering complex vulnerabilities that automated tools miss and generating the exploitation evidence auditors require.
Schema-based testing and API fuzzing validate input handling robustness across a broad input space, providing strong evidence of input validation controls for PCI DSS compliance.
Authentication and authorization validation verifies that access controls function correctly across all endpoints, addressing the vulnerability class most commonly cited in compliance audits.
Compliance-mapped reporting ties every finding directly to the relevant PCI DSS requirement, GDPR article, or SOC 2 Trust Services Criterion, eliminating the interpretive work that slows down audits.
CI/CD pipeline integration embeds API security testing into the development lifecycle, enabling continuous compliance readiness without slowing deployment velocity.
Final Thoughts
API security compliance is a technical requirement that cannot be satisfied through documentation alone. PCI DSS, GDPR, and SOC 2 all expect organizations to demonstrate that their APIs are actively secured, continuously tested, and capable of withstanding real-world attack scenarios.
The organizations that achieve and maintain compliance most efficiently treat API security as an ongoing program rather than a periodic exercise. They integrate automated testing into their deployment pipelines, conduct regular manual penetration testing, maintain detailed remediation records, and keep auditors supplied with structured, evidence-based reports.
A reactive approach to API security creates compliance gaps, delays certifications, and leaves organizations exposed to the exact threats that frameworks like PCI DSS, GDPR, and SOC 2 were designed to prevent. A proactive, continuous approach turns compliance into a baseline capability that scales alongside the organization.
Want this tested on your own stack?
Pre-book a penetration test or SOC 2 / ISO 27001 readiness. No payment and no commitment.
 Questions about scoping?