Security notes from the people who do the testing.
Penetration testing, SOC 2 and ISO 27001, and the fixes that actually close findings. Written for engineers and founders who have a security review coming up.
 · nyxsentinel
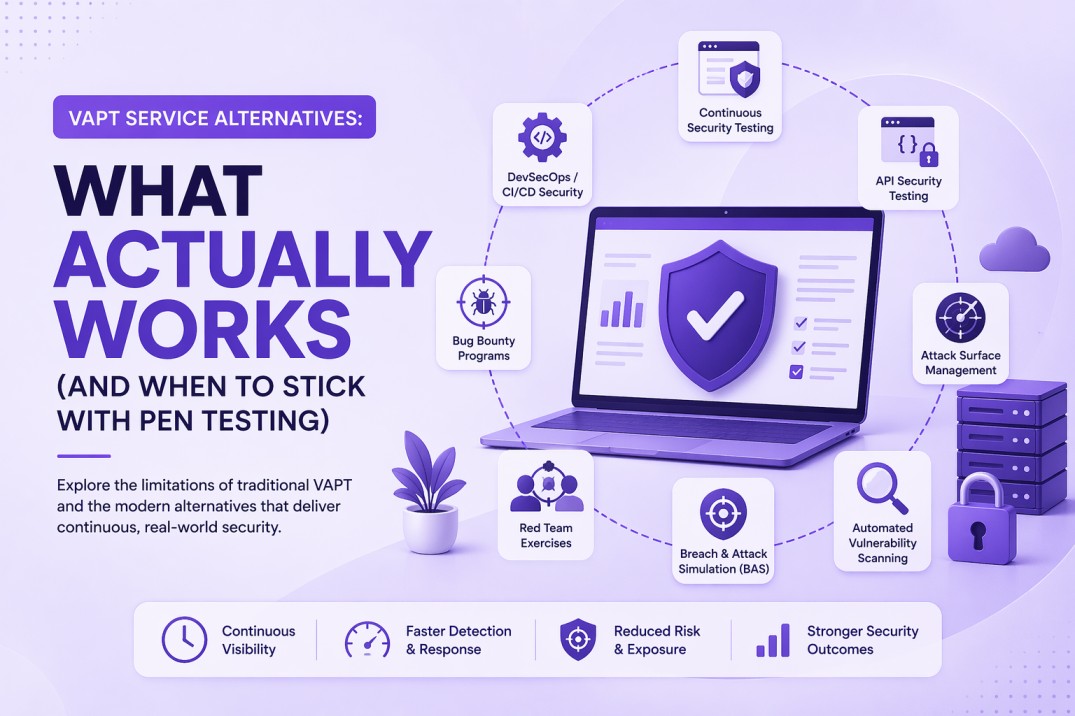
Beyond Traditional VAPT: 8 Modern Alternatives That Close the Gaps Periodic Testing Leaves Open
If you've been relying on periodic penetration testing alone to secure your infrastructure, you're already behind. The way modern applications are built, microservices, containerized workloads, API-first architectures, and continuous deployments, means your…
Read article →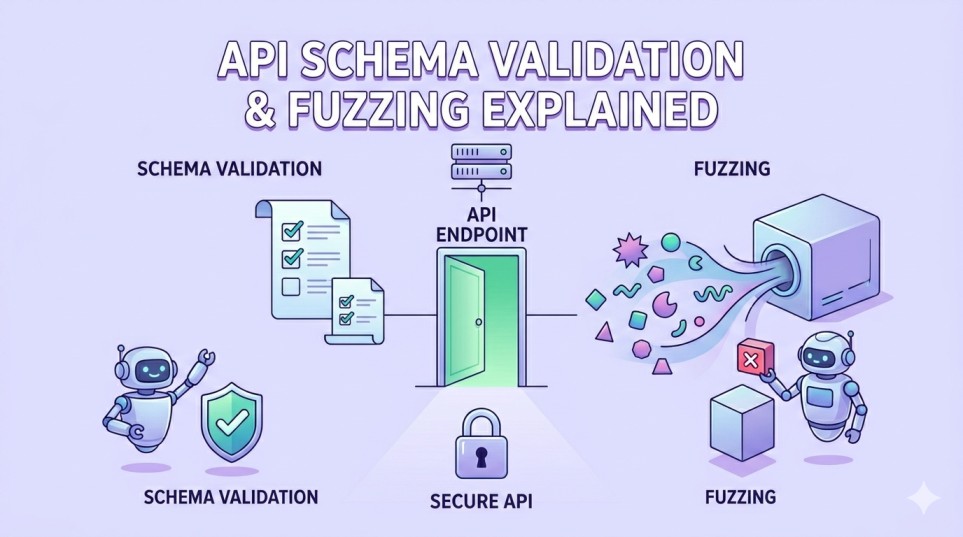 · nyxsentinel
API Schema Validation and Fuzzing: How to Catch the Vulnerabilities That Standard API Testing Leaves Behind
Modern APIs expose critical data, power business workflows, and connect multiple services across distributed systems. Even a single weak endpoint can…
Read article → · nyxsentinel
VAPT for SaaS Companies: How to Find Vulnerabilities, Protect Multi Tenant Data, and Pass Security Audits
SaaS applications run on shared infrastructure, expose APIs, and ship updates frequently. Each factor increases the risk of security gaps that…
Read article → · nyxsentinel
OWASP API Security Top 10 (2023): Risks, Examples, and Prevention
APIs sit at the center of modern software. Mobile apps, SaaS platforms, and microservices all rely on them to exchange data and trigger actions. In…
Read article → · nyxsentinel
Web Application Penetration Testing: How It Works, What It Covers, and When You Need It
Web applications power logins, payments, and customer data, which makes them a common target for cyber attacks. Web application penetration testing…
Read article →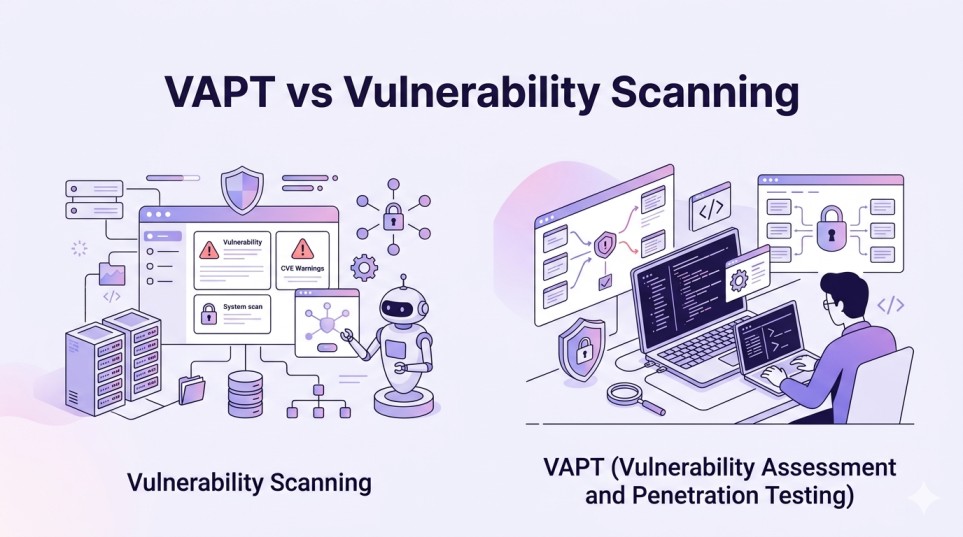 · nyxsentinel
VAPT vs Vulnerability Scanning: What’s the Difference?
Organizations use security testing to identify weaknesses before attackers exploit them. Two terms often appear in that context: VAPT ( Vulnerability…
Read article →Rather have us test it than read about it?
Pre-book a penetration test or compliance readiness. No payment and no commitment.
 Questions about scoping?